RGB’s Private Consensus: Client-Side Validation, Explained Simply
RGB Hub recorded this conversation on an X Space on September 2, 2026, launching a new explainer series for people with no technical background. The guest was Ron (Shuning Hong), Chief Scientist at BiHelix and one of the earliest people to write about RGB Protocol on Bitcoin in Chinese. The topic was client-side validation itself — the idea RGB Protocol on Bitcoin is built on.
In Brief
- Client-side validation is best understood as RGB private consensus — only the two people in a transaction verify it, instead of every node on a public blockchain
- It sits at the end of a long human history of reaching agreement: forced consensus (power, law), voluntary consensus (handshake deals, signed contracts, trusted third parties), and now blockchain’s public consensus
- On Bitcoin’s chain, an RGB transaction leaves behind only a small commitment — a cryptographic hash, not the actual deal
- Upside: no redundant computation across nodes, plus privacy by default. Downside: only two parties hold the data. If you lose it, you lose the proof.
- Asset issuance is RGB’s least important feature — its real value is Turing-complete smart contracts, backed by Bitcoin’s security and Lightning’s throughput
What Is RGB’s Private Consensus in the Simplest Possible Terms?
Ron prefers to describe client-side validation as private consensus, defined against blockchain’s public consensus.
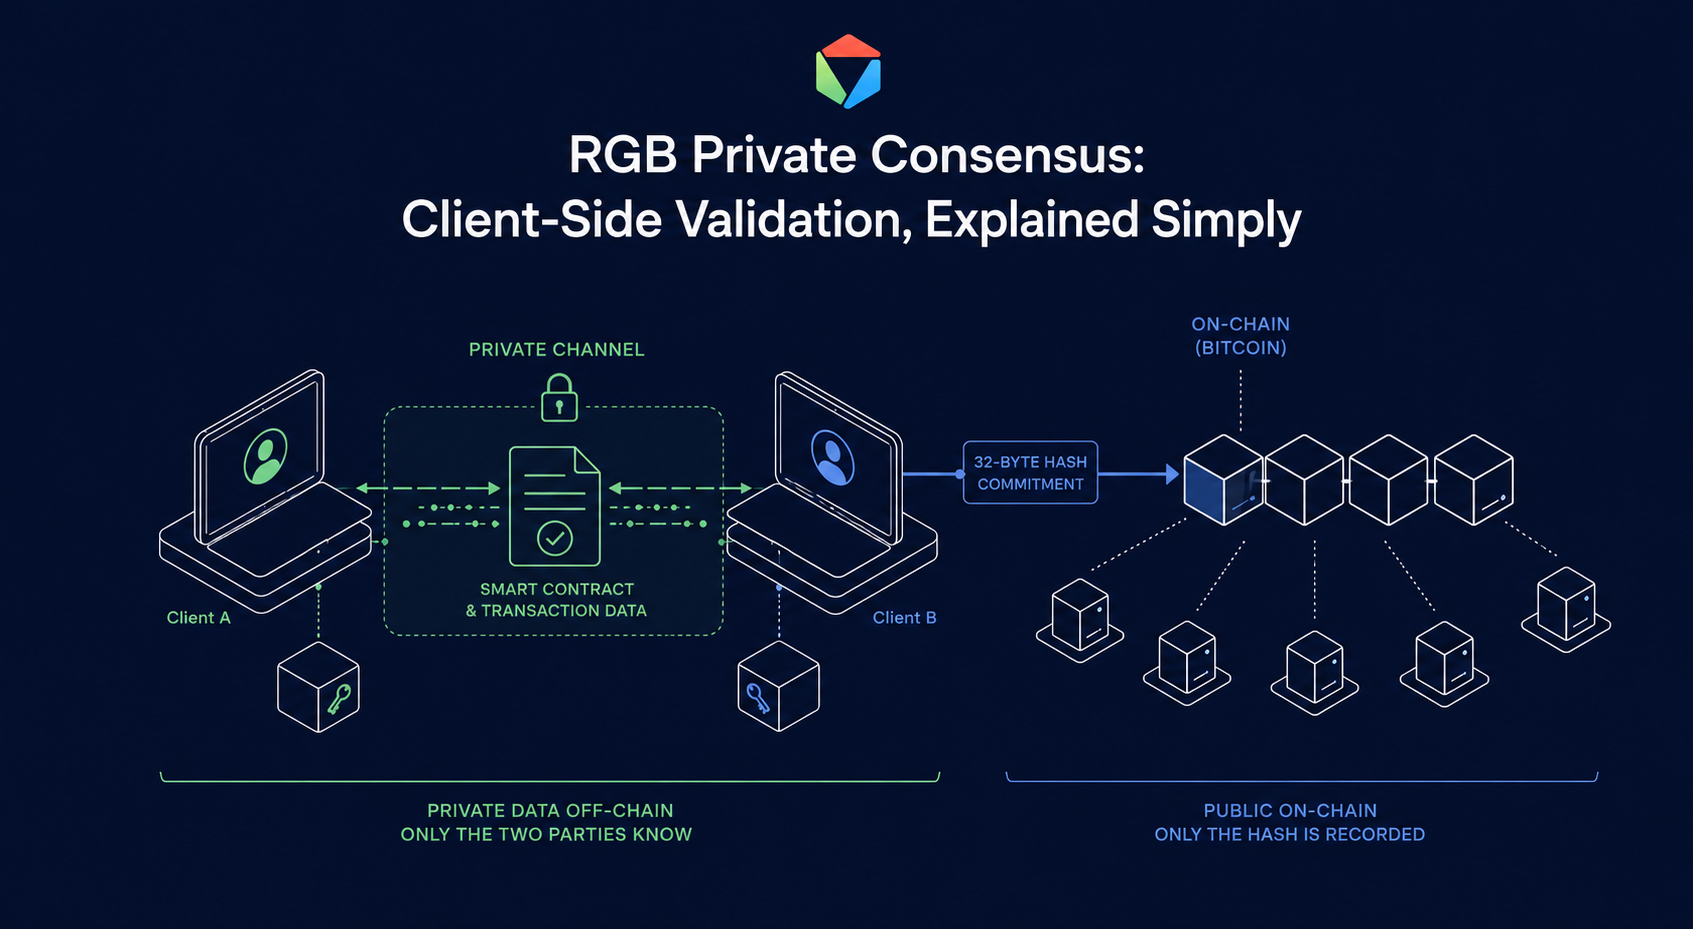
Public consensus is the base of Bitcoin, where countless miners run the same work and package the same block. Once more than half of them agree, the transaction is final. Client-side validation, though, runs the opposite way: the two parties in a transaction verify it themselves, privately, with nobody else involved. So two people reach an agreement, and the whole process ends there.
Validation itself just means proving something is real and hasn’t been tampered with, while “client-side” simply means the users transacting. If two people are involved, there are two clients doing the verifying (sometimes more, but two is the simplest case).
Put together, the definition becomes the following: two people privately verifying, between themselves, that what they’re agreeing to is real and unaltered. Thus, client-side validation corresponds exactly to the idea of private consensus.
Besides Client-Side Validation, What Are Other Ways to Reach Consensus?
Client-side validation is one method among many that have been used to reach agreement. In broad terms, they fall into two families.
Forced consensus is the oldest: whoever holds power decides, and the other side has no real choice but to go along. War, slavery, government authority, even law fall into this category. Law is still a form of forced consensus, since it relies on the state’s police and courts to enforce it. It works, but it’s inherently unfair, and unfairness makes it inefficient at scale. So over time, human societies have drifted toward less forceful versions of it (a rule-of-law society is still technically forced consensus, just a much softer version).
Voluntary consensus is the alternative, where people agree because they choose to, not because they’re compelled to. The earliest form was probably barter: two people striking a deal on the spot. This type of arrangement is a gentleman’s agreement, and it has an obvious weak point: nothing guarantees the other side actually delivers. So humans invented ways to reinforce it, by inserting the terms in a written document, signing it, and sealing it (a distinctly Chinese practice, alongside the signature), effectively creating something that leaves a trace if someone tries to tamper with it in the future.
Alongside those harder safeguards, people started using a softer kind of reinforcement: morality, religion, and the social pressure to keep your word. And in modern commerce, the dominant method became the trusted third party (a bank, a notary, a well-known institution that vouches for both sides). Almost all of today’s commerce runs through some trusted third party.
When you deal with a third party, the need for trust becomes very important. A central bank is a trusted third party too, since everyone assumes it won’t print money recklessly. However, the moment it does, the currency loses value, and those who possess it become poorer.
Satoshi Nakamoto precisely tackled this issue with Bitcoin: a new kind of consensus that needs no gentleman’s agreement and no trusted third party, reached instead through cryptography and thousands of miners publicly agreeing on the same ledger.
Blockchain solved the trust problem, but it created a new one, since it’s radically public. The kind of private, one-on-one dealing that a handshake or a signed contract allowed simply doesn’t fit on a transparent ledger. Client-side validation closes that gap, though, as it keeps blockchain’s core advantage (no trusted third party required) while restoring the privacy of a private agreement. In other words, it’s what you get when you combine a blockchain with a private, off-chain deal.
What Is Inserted on the Bitcoin Blockchain?
Client-side validation isn’t unique to RGB, since Taproot Assets uses it too, but RGB was one of the first serious attempts to combine it with Bitcoin directly.
Satoshi never designed Bitcoin transactions to carry a memo the way a bank transfer does. Even so, his design eventually made room for a small one: rather than attaching the actual content to a transaction, you attach a hash of it in an OP_RETURN output, as a proof that specific content exists and is unaltered, without publishing the content itself.
For a long time, Bitcoin nodes only relayed small amounts of data this way by default (on the order of tens of bytes), but that small amount was more than enough to hold a hash.
Around 2013–2014, “colored coins” reinterpreted ordinary bitcoin transactions as transfers of some other asset, and the earliest version of USDT launched this way. Colored coins eventually faded when faster chains arrived, but the same underlying method (using Bitcoin transaction data to represent something beyond plain BTC transfer) resurfaced later through other mechanisms that could carry far more data on-chain, driving a large share of recent Bitcoin transaction volume toward non-monetary use.
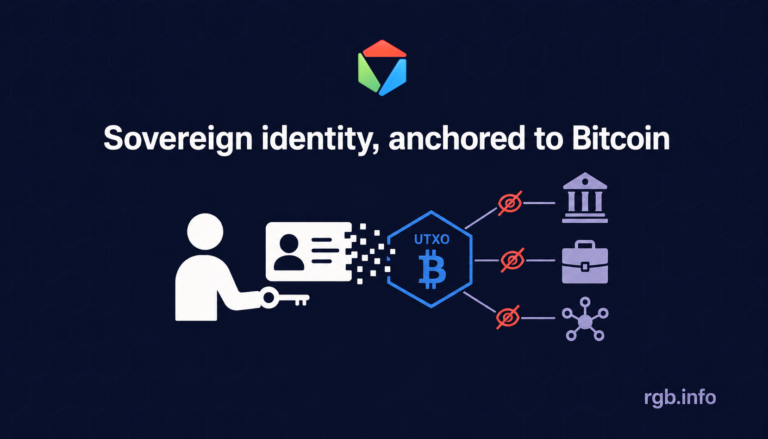
RGB takes a much narrower approach of that idea. An RGB transfer, whether it’s a simple asset transfer or a full smart contract execution, commits to Bitcoin’s chain as a single 32-byte hash (a cryptographic commitment, not a zero-knowledge proof). That commitment is publicly verifiable by anyone, since it proves something happened, but the actual content (what was transferred, to whom, under what terms) stays off-chain, known only to the parties involved. So the answer to “what’s on the chain when an RGB transfer happens” is almost nothing: a tiny, tamper-proof fingerprint, and nothing more.
What Problems Does This Actually Solve for a Business?
Two, concretely.
Redundant computation. Bitcoin today runs on well over 200,000 nodes, and all of them process and agree on every single transaction, meaning 200,000 different nodes would recompute the same routine business logic if it lived directly on-chain. The duplication is enormous, and it’s the core reason blockchain throughput is so limited. Client-side validation, by contrast, only requires the two counterparties to process a given transaction, since other nodes never even see that it happened: they only know that a Bitcoin transaction occurred. So performance goes up, simply because the redundancy disappears.
Privacy. Every Bitcoin address and its full transaction history is public by default, and researchers can already trace over 70% of Bitcoin addresses today back to a real identity. There’s effectively no privacy on-chain unless you go out of your way to protect it, and doing it well is genuinely hard. On the contrary, client-side validation restores privacy as the default: nobody outside the transaction knows it happened, let alone what it involved, unless the parties choose to disclose it.
Is There a Downside, Compared to Putting Everything On-Chain?
Yes, and Ron was direct about it: client-side validation trades redundancy for privacy, but with a real cost.
On Bitcoin, your transaction data lives on 200,000+ nodes, so for all practical purposes, it can’t be lost. With client-side validation, though, the record of a transaction exists only where the two parties keep it: two copies, full stop. It’s like signing a paper contract in duplicate. If you lose, damage, or corrupt your copy, and the other side won’t produce theirs, you have no way to prove the transaction ever happened. So whatever asset you received through this process is effectively gone.
Ron laid out three ways to think about protecting something valuable — say, a gold bar:
- A trusted third party — deposit it in a bank vault. Safe and convenient, but you’re trusting the bank not to default or embezzle, with little recourse if it does.
- Full public exposure — display it in the middle of a public square, guarded around the clock and livestreamed to the world. Nobody can steal it because everyone is watching, but you’ve paid a fortune for security and given up all privacy. This approach is blockchain.
- Full self-custody — lock it in your own home safe. Private, and nobody but you can betray your own trust — but if the safe is destroyed, the gold goes with it. This approach is client-side validation.
Regarding this issue, BiHelix is building a system with separate ownership from custody of the data itself. You keep the private key (true ownership) entirely in your own hands, while a professional custodian holds the underlying asset data on your behalf. A private key is much easier to safeguard than the full data trail behind a complex, high-value transaction. So, it meaningfully reduces the odds that an ordinary user loses everything to a lost device.
Why Build on RGB Instead of a Simpler Alternative, Like Taproot Assets?
If RGB’s only real use were issuing tokens (stablecoins, memecoins, whatever) there would be little reason to prefer it over Taproot Assets, which does asset issuance with far less technical overhead.
Asset issuance is actually the least important thing RGB does. What RGB is actually built for is Turing-complete smart contracts: arbitrary business logic, DeFi, any commercial arrangement two or more parties want to encode, not just a transfer of value. So smart contracts are a categorically different capability than issuing a token.
The reason to build that on top of Bitcoin specifically, rather than anywhere else, comes down to what Bitcoin already constitutes: fifteen-plus years of uninterrupted uptime, hundreds of millions of users, trillions of dollars in value, and a legal status edging toward reserve-currency territory in some jurisdictions.
So, anything built on RGB inherits that installed base as a potential market from day one. When you add Lightning Network on top, then you can create an infrastructure based on the combination of RGB, Lightning and Bitcoin that is capable of hosting commerce at global scale.
For the full technical breakdown, see our guide to client-side validation.
Further Reading
Recorded on an X Space, September 2, 2026, the first episode of RGB Hub’s Chinese-language explainer series. The original conversation was conducted in Chinese; this piece is an English adaptation. Ron (Shuning Hong) is Chief Scientist at BiHelix.